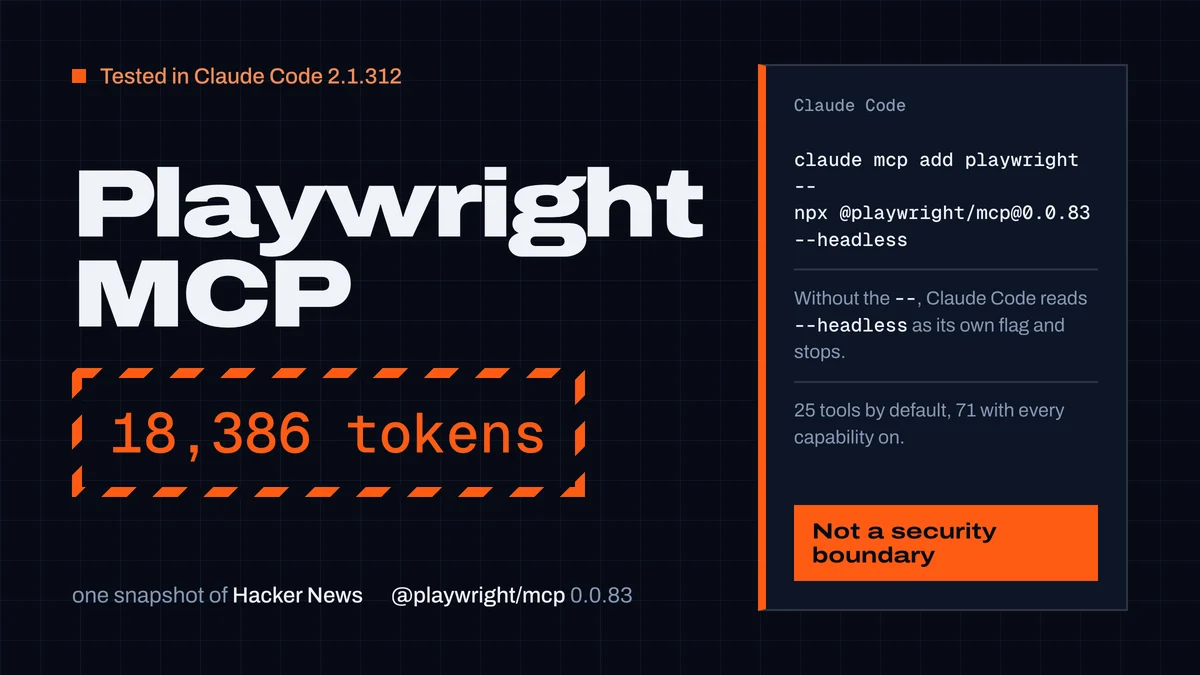
Guides
Playwright MCP server: setup in Claude Code, Codex and Cursor
Set up the Playwright MCP server in Claude Code, Codex and Cursor with tested commands, plus its 25 tools, snapshot token costs and safe settings.
CodexGuild Research13 min read
For Claude Code, Codex, Cursor and every MCP agent
CodexGuild checks your coding agent’s work before it reaches production. Fake and vulnerable packages, removed APIs, poisoned skills and dangerous commands are stopped as they happen, and the agent can’t call a task done until the code is checked.
Free on Free, no card. Only package names and versions leave your machine, never your code.
Task done
Checked. Changed code was never tested. Ran npm test first: 48 passed.
5 stopped before production
 CodexCursorGemini CLIOpenCode
 HermesCopilotWindsurfClineKimi Code
 OpenClaw
 Aider
Vibe coding finds the problems after release. A guarded agent meets each one at the step where it starts, while it is still cheap to fix.
MCP, every session
The agent works from last year's knowledge and has no idea your lockfile pins a vulnerable version.
Security check-up
Advisories for the exact versions you run with the release that fixes them, new breaking releases, flagged skills already installed.
Claude Code hook
It calls an API your version removed. Fine in its memory, broken in your build.
Write guard
A removed API stops the write and comes back with the replacement. Deprecated ones get a warning.
MCP or Claude Code hook
It installs a name it made up, a typosquat, malware or a version with a known vulnerability.
Package guard
Every package is checked against the registry and advisories first. Fake and malicious ones are blocked, vulnerable ones come with the fixed version.
MCP and website
It copies a SKILL.md or MCP config with hidden instructions that read your keys.
Skill scan and MCP inspection
Scanned for prompt injection, credential theft, hidden Unicode and tool poisoning, then installed byte for byte.
Claude Code hook
It deletes a folder, resets a database, force-pushes or sends a secret to a remote host.
Command limiter
The commands you never want an agent to run are blocked on your machine, before the shell sees them.
Claude Code hook
It reports the task finished without running a single test.
Done gate
No finish while changed code is unchecked. It runs your tests or type-check first, or says what it couldn't verify.
GitHub App, Team
A new dependency with a known vulnerability slips through review.
PR checks
A CodexGuild check on every pull request: blocked packages, newly vulnerable versions, removed APIs.
Dashboard
A new advisory lands on a version that is already in production.
Project watch
Your manifests and GitHub repositories are watched for new advisories and breaking releases, with no agent running.
Same agent, same model. The difference is what it knows and what it is allowed to skip.
A guarded agent also wastes less. It stops guessing at APIs that changed, gets the known fix for an error instead of looping, and keeps the lessons from its own corrected mistakes. We measured it on the same model with and without CodexGuild.
error TypeError: useFormState is not a function
versions react 19.1.0, next 15.5.0
Removed in react 19.0.0
ReactDOM.useFormState → React.useActionState
Verified fix React 19 form actions
Import useActionState from react. Same arguments, plus isPending.
Also returned: how many other accounts hit this error in the last 30 days.
Instead of trying variation after variation, the agent asks for the known fix for that error in your versions. Fewer loops, fewer tokens, less waiting. Secrets are stripped before anything is looked up.
How error lookup worksBefore the first prompt, the agent reads your manifests and asks CodexGuild what is wrong with this exact project: vulnerable versions and the release that fixes them, new breaking releases, flagged skills you already installed.
synced just now · 212 npm dependencies, all exactExample
Releases since last sync
prisma 6.19 → 7.10.0breaking?
Installed skills
1 flagged · 41 passed
One connection fits the set. Each part does one job, and you can read exactly how it works.
Deprecated APIs
Search what was removed or deprecated, by library and version.
Instruction linter
Check AGENTS.md and CLAUDE.md for size, secrets and leftovers.
Models and benchmarks
Prices, context windows and coding benchmarks with dates.
Free tools on the website, no account needed.
Every account starts on the free Free plan with the core guards. Higher plans add projects, team checks and more daily capacity.
The base guards: session check-up, package checks, local command and done gates, a few error lookups a day.
3 error lookups, 25 freshness checks
Safe intake: scanned skills and MCP servers, GitHub projects watched for advisories.
10 error lookups, 120 freshness checks
Full knowledge: known fixes and fresh library facts all day long.
200 error lookups, 800 freshness checks
The whole team on one stage: shared projects and alerts, checks on every pull request.
1000 error lookups, 5K freshness checks
You create a key, the agent installs the rest. Nothing to maintain.
Free, in the dashboard. One key per agent.
Dashboard → Agents → New agentPaste one sentence into your agent. It connects itself and asks before changing anything.
Set up CodexGuild on this machine: read https://api.codexguild.com/v1/start-here.md and follow "0. First-time setup". My agent key is in $CODEXGUILD_API_KEY — never print it. Ask me before you change any config.Every session starts with a security check-up, and the guards run on their own.
codexguild_syncLangGraph: Unencoded identifiers in LangGraph SDK v3 streaming can redirect authenticated GET requests
Oct 28, 2026
Model Context Protocol Python SDK: Server bearer-token authentication accepts tokens issued for a different resource server
Oct 27, 2026
Model Context Protocol Python SDK: HTTP client transports followed cross-origin redirects carrying custom headers and bodies
Oct 27, 2026
Releases and incidents your agent can't know about yet, tested.
Guides
Set up the Playwright MCP server in Claude Code, Codex and Cursor with tested commands, plus its 25 tools, snapshot token costs and safe settings.
CodexGuild Research13 min read
Guides
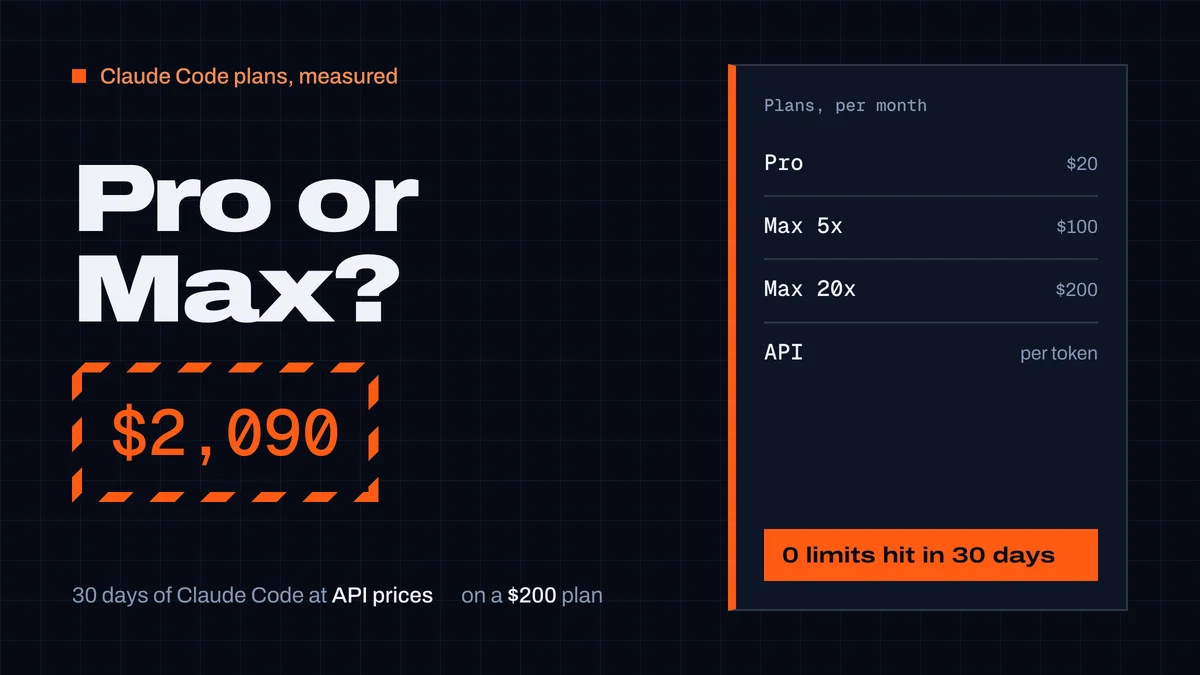
Claude Pro vs Max for Claude Code: prices, how the 5-hour and weekly limits work, and our measured month: $2,090 of usage at API prices on a $200 Max plan.
CodexGuild Research9 min read
Guides
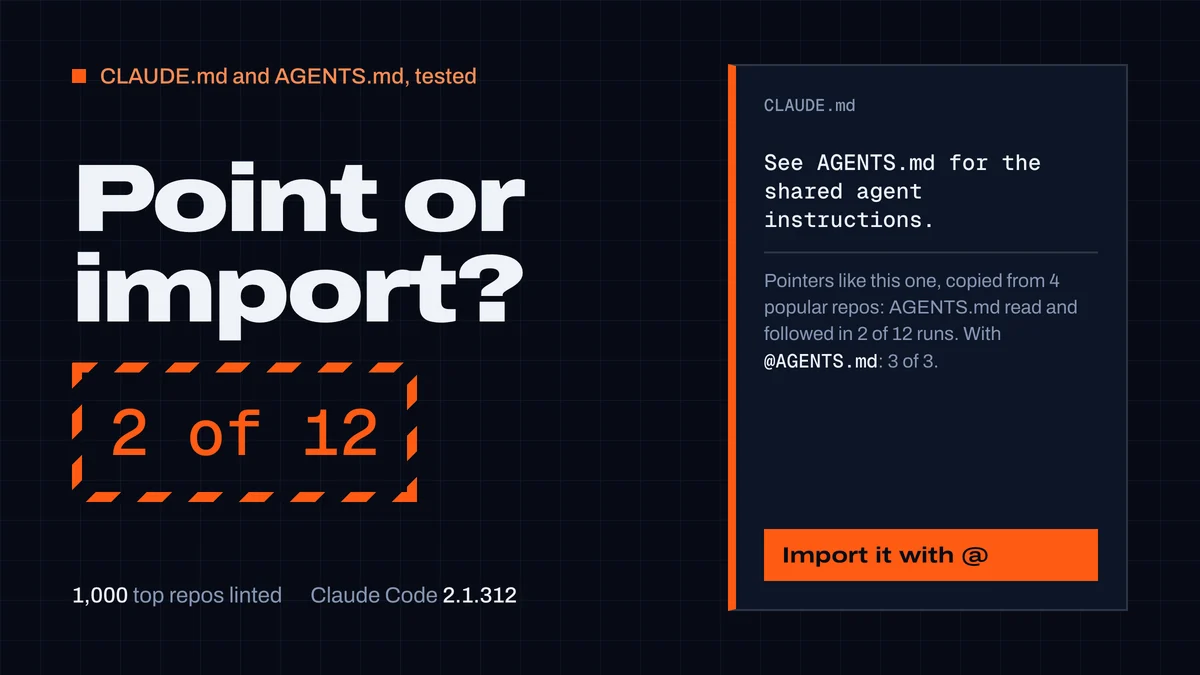
What to put in a CLAUDE.md or AGENTS.md and how to keep both. We linted 1,000 top repos and tested Claude Code: "See AGENTS.md" worked 2 times in 12.
CodexGuild Research14 min read
What the tune changes, what it costs and what it never touches.
CodexGuild makes AI coding agents code safely before anything reaches production. One connection guards Claude Code, Codex, Cursor, Gemini CLI, Hermes and other agents: they learn what changed in the libraries you use, check packages before installing them, use only security-scanned skills and MCP servers, are stopped before dangerous commands, run your tests before calling a task done and look up known fixes for errors instead of guessing.
Agent skills are folders with a SKILL.md file (plus optional scripts) that teach a coding agent how to do a specific task — deploy to a platform, write tests in a framework, follow a design system. Claude Code, Codex, Hermes Agent, OpenCode and Gemini CLI all load the same SKILL.md format.
Connect Claude Code to the CodexGuild MCP server and run codexguild_sync at the start of a session. It returns releases and breaking changes for the exact versions in your project since the last sync, so the agent stops writing code against APIs that have changed since it was trained.
It calls codexguild_debug with the error and its package versions. CodexGuild returns the known fixes for that error — verified knowledge-base entries and APIs that were removed in those versions — and how many others hit it recently. Secrets are redacted first and only the normalized error line is stored.
Yes. CodexGuild is a remote MCP server (Streamable HTTP with a Bearer key) plus an Agent Skills–format skill, so it works with Hermes Agent, Codex CLI, Claude Code, OpenClaude, OpenCode, Kimi Code, OpenClaw, Gemini CLI, Cursor, GitHub Copilot, Windsurf, Cline and Aider. The Connect page shows the exact config for each harness.
Every skill is statically scanned before it is listed — for pipe-to-shell, credential exfiltration, hidden Unicode, prompt injection, agent-config tampering and safety bypasses. Only scan-passed skills are served for installation, byte-identical to the files that were scanned. Flagged skills stay visible with their findings.
Yes. The Free plan is free forever for one developer: read everything, sync every session, check packages, look up a few known fixes a day and install scanned skills. Guard adds GitHub projects and alerts, Pro all-day error lookup and freshness, Team a whole team on one stage.
Start on Free for free. Move up a plan when your projects and team grow.